CAAV to trial biometric authentication at Van Don airport
HCMC – Following a test operation at the Cat Bi International Airport in Haiphong City, the Civil Aviation
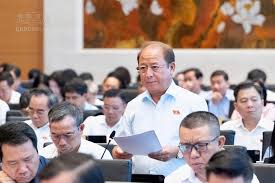
As artificial intelligence (AI) becomes increasingly integrated into biometric authentication processes, the question of accountability for errors has gained prominence. During a recent session of the National Assembly, lawmakers emphasized the need for regulations that would ensure AI service providers share responsibility for damages resulting from authentication errors due to technical flaws.
Representative Sùng A Lềnh from Lào Cai raised concerns regarding the legal responsibilities associated with AI applications in biometric verification. The draft law stipulates that organizations and individuals who utilize AI-based identification and authentication systems must ultimately bear responsibility for their decisions based on the results produced by these systems. However, Lềnh argued that it is essential to clarify that AI service providers should also be held jointly responsible for compensating damages if errors arise from technical vulnerabilities or system failures, except in cases of intentional misconduct or fraud by the user.
Another representative, Nguyễn Thị Việt Nga from Hải Phòng, highlighted the importance of data security, especially as data becomes increasingly intertwined with the operations of government agencies, businesses, and the daily lives of citizens. She warned that any incident leading to data breaches, distortions, or interruptions could have severe consequences. Before presenting the draft law to the National Assembly, Nga suggested creating a comprehensive list of specific procedures that need to be followed and aligning these with existing laws on data, cybersecurity, and personal data protection.
Additionally, she stressed the necessity of establishing binding principles within the law to prevent organizations and individuals from having to repeat verification processes for the same subject or information already confirmed by competent authorities. There should also be clear guidelines on the responsibilities of different agencies to ensure that individuals are not left to prove their compliance with various procedural obligations.
Representative Nguyễn Đặng Ân from Lạng Sơn pointed out that the draft law includes provisions for protecting data during sharing, providing, and transacting processes, which must correspond to the data's sensitivity level. He urged for clearer principles to be established to ensure consistency between the three relevant laws, avoiding potential misunderstandings.
The draft law also outlines specific measures for reporting, handling, investigating, and recovering data following security incidents. However, there are calls for further review regarding how individuals affected by data security breaches are informed so they can proactively protect their rights. It may be beneficial to empower the government to set appropriate regulations regarding the content and methods of informing affected individuals, ensuring they are aware of risks related to their data and the necessary steps to safeguard themselves.